


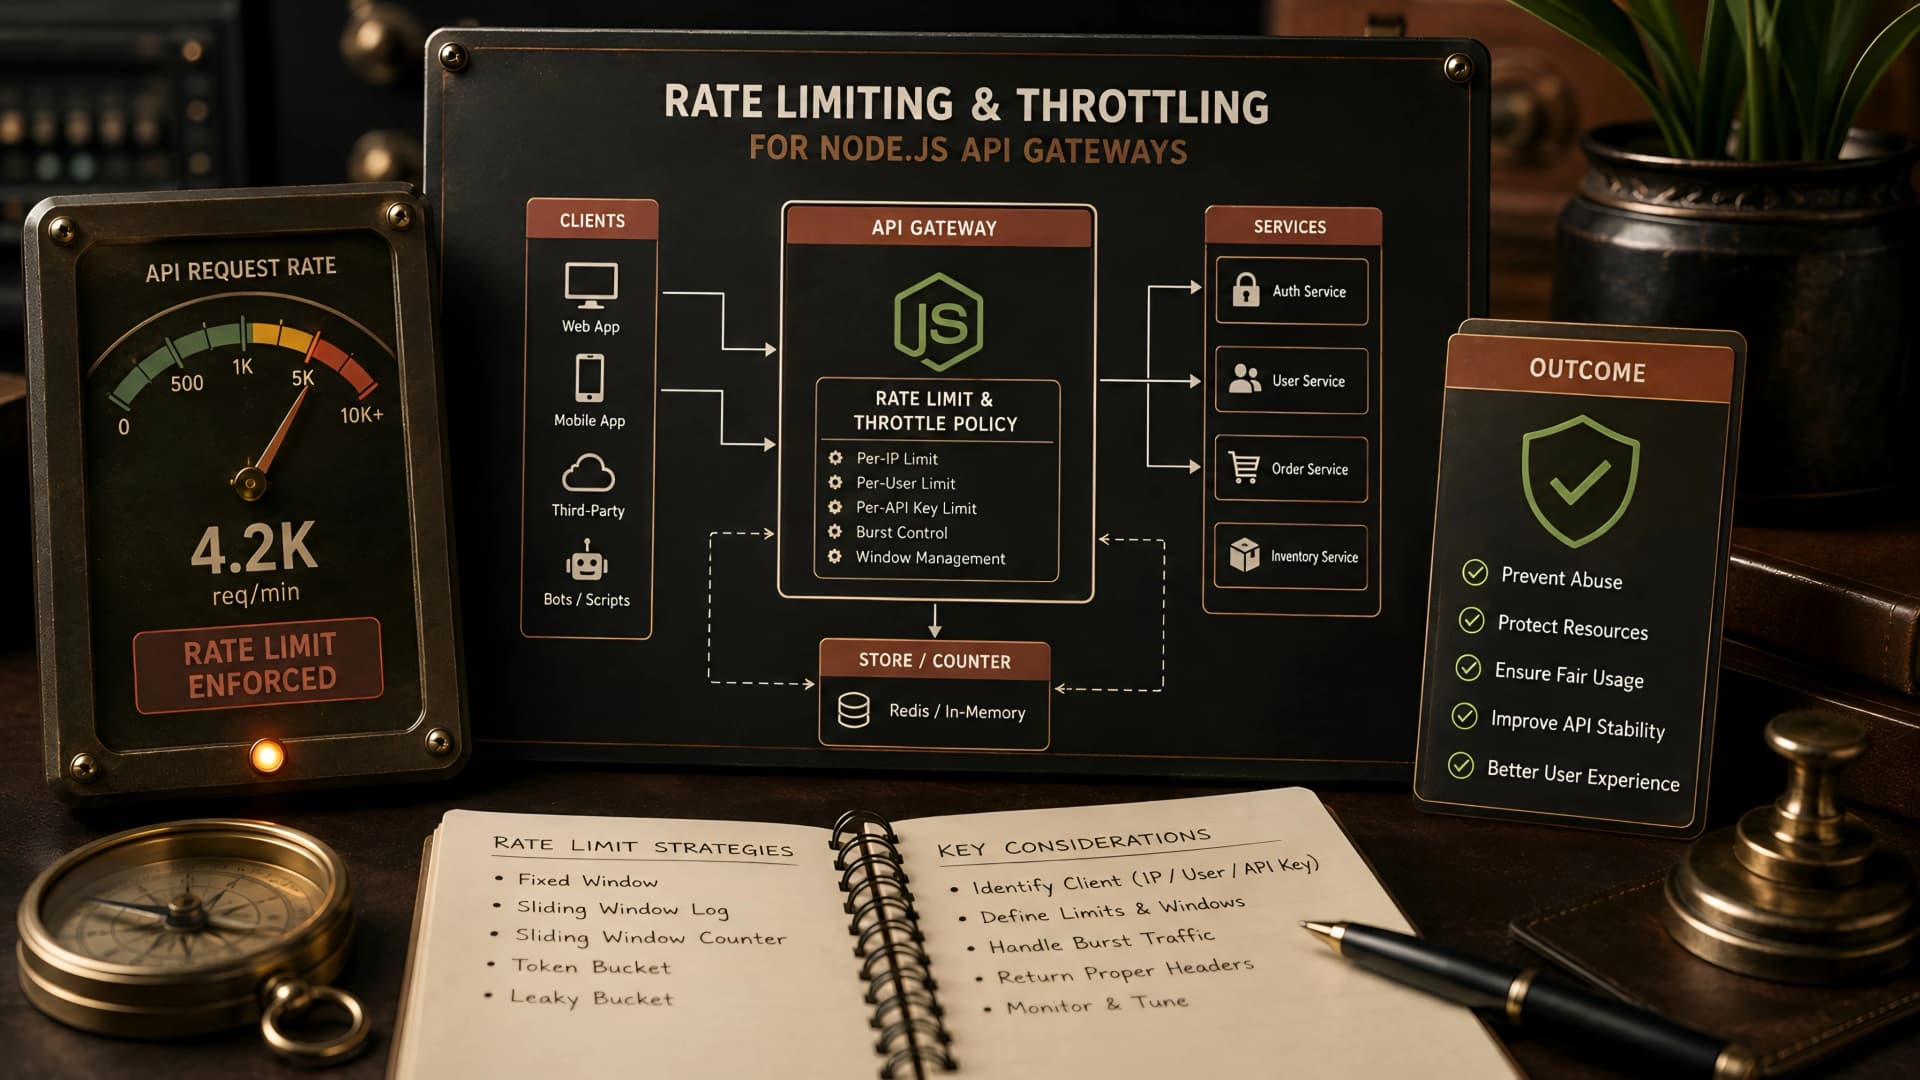
Uncontrolled access to your API can quickly spiral into a nightmare. Whether it's a denial-of-service attempt, data scraping, or simply an overzealous client, the consequences are always the same: degraded performance, resource exhaustion, and a frustrating experience for legitimate users.
This is where rate limiting and throttling become indispensable. Within a Node.js API Gateway architecture, these mechanisms act as crucial gatekeepers, ensuring fair usage and protecting your backend services from undue stress. Implementing them thoughtfully is a hallmark of robust engineering.
Why Rate Limiting is Critical for Node.js APIs
Imagine a scenario where a single client script goes rogue, firing thousands of requests per second at your API. Without rate limiting, your Node.js server could quickly become overwhelmed, leading to slow responses or even crashes for everyone else.
Rate limiting enforces a ceiling on the number of requests a user or IP address can make within a defined timeframe. This prevents resource starvation and helps maintain the stability and responsiveness of your API. It's a proactive measure against both malicious attacks and unintentional abuse.
Understanding Rate Limiting Strategies
Choosing the right strategy for Node.js API rate limiting depends on your specific needs and the nature of your application. Each approach has its tradeoffs in terms of accuracy, resource usage, and complexity.
The most common strategies include Fixed Window, Sliding Window Log, and Sliding Window Counter. At Muhyo Tech, we evaluate these based on the API's traffic patterns and the desired fairness level for each client, considering the operational overhead.
Fixed Window Counter
This is the simplest strategy. It defines a fixed time window (e.g., 60 seconds) and counts requests within that window.
Once the limit is reached, all subsequent requests within that window are blocked. The main drawback is a potential 'burst' problem right at the start or end of a window, where a client might make many requests in quick succession across two windows.
Sliding Window Log
More precise, this strategy keeps a timestamp log of all requests made by a client. When a new request arrives, it removes all timestamps older than the current window and then checks the count.
This method offers excellent accuracy and avoids the burst issue of the fixed window. However, it can consume more memory, especially for high-traffic APIs, as it stores individual request timestamps.
Sliding Window Counter
This strategy combines the efficiency of the fixed window with the smoothness of the sliding window. It divides the time into smaller buckets and uses an average to approximate the rate.
It's a good compromise between accuracy and memory usage, often implemented by taking a weighted average of the current window's count and the previous window's count. This is a common choice for production systems where balancing resources is key.
Implementing Rate Limiting in Node.js with Middleware
For Node.js applications, especially those built with Express.js, middleware offers a clean and effective way to implement rate limiting. Packages like express-rate-limit provide a solid foundation for this.
When integrating into an API Gateway, this middleware typically sits early in the request processing pipeline. This ensures that unauthorized or excessive requests are rejected before they consume valuable backend resources.
const rateLimit = require('express-rate-limit');

const apiLimiter = rateLimit({
  windowMs: 15 * 60 * 1000, // 15 minutes
  max: 100, // Limit each IP to 100 requests per windowMs
  message: 'Too many requests from this IP, please try again after 15 minutes',
  standardHeaders: true, // Return rate limit info in the `RateLimit-*` headers
  legacyHeaders: false, // Disable the `X-RateLimit-*` headers
});

// Apply the rate limiting middleware to all requests
app.use(apiLimiter);
This basic setup applies a global rate limit. For more granular control, you might apply different limits to specific routes or user roles. For instance, authenticated users might have a higher limit than unauthenticated ones.
Distributed Rate Limiting with Redis
In a horizontally scaled Node.js API Gateway environment, where multiple instances of your gateway are running, a simple in-memory rate limiter won't work. Each instance would maintain its own count, leading to inconsistent and ineffective limits.
This is where a distributed store like Redis becomes essential. Redis's atomic operations and high performance make it ideal for storing and incrementing request counts across multiple gateway instances. We often use Redis for this purpose to ensure consistency and reliability.
const RedisStore = require('rate-limit-redis');
const { createClient } = require('redis');

const redisClient = createClient({
  url: 'redis://localhost:6379',
});

redisClient.on('error', (err) => console.error('Redis Client Error', err));
redisClient.connect();

const limiter = rateLimit({
  store: new RedisStore({
    sendCommand: (...args) => redisClient.sendCommand(args),
  }),
  windowMs: 60 * 1000, // 1 minute
  max: 100, // 100 requests per IP per minute
});

app.use(limiter);
Using Redis ensures that every gateway instance consults a single, consistent source of truth for rate limits. This is crucial for maintaining fair and accurate throttling across your entire distributed system.
Advanced Considerations and Best Practices
Implementing Node.js API rate limiting effectively goes beyond just setting a maximum request count. Consider these advanced points for a robust system.
Proper identification of clients, clear error messaging, and robust monitoring are all critical for a well-rounded solution. This reflects our standards at Muhyo Tech when designing scalable systems.
Identifying Clients
Rate limiting often relies on identifying the client making the request. IP addresses are common, but they can be problematic with shared NATs or proxies. Consider using API keys, authenticated user IDs, or a combination of factors for more accurate and fair limiting.
A multi-factor approach to client identification can prevent legitimate users from being unfairly throttled due to shared IP addresses. This improves user experience without compromising security.
Throttling vs. Rate Limiting
While often used interchangeably, there's a subtle difference. Rate limiting strictly blocks requests once a threshold is met. Throttling, on the other hand, might delay or queue requests, allowing them to proceed once capacity is available.
Throttling is particularly useful for background tasks or non-critical operations where a slight delay is acceptable. It helps smooth out demand spikes without outright rejecting requests.
Clear Error Responses and Headers
When a client is rate-limited, provide clear HTTP status codes (e.g., 429 Too Many Requests) and informative headers (Retry-After, X-RateLimit-Limit, X-RateLimit-Remaining, X-RateLimit-Reset). This helps clients understand why their request was denied and how to proceed.
Good communication through HTTP headers reduces client-side errors and improves the overall developer experience for those consuming your API. It's a small detail that makes a big difference in usability.
Monitoring and Alerting
Once deployed, monitor your rate-limiting mechanisms. Track blocked requests, identify patterns of abuse, and adjust your limits as needed. Set up alerts for sustained high rates of blocked requests.
Effective monitoring allows you to fine-tune your limits and identify potential security threats or changes in user behavior early on. This continuous feedback loop is vital for maintaining API health.
Conclusion: A Pillar of API Reliability
Implementing rate limiting and throttling is not just a defensive measure; it's a fundamental aspect of building reliable, scalable, and fair Node.js APIs. It protects your infrastructure, ensures consistent performance, and contributes directly to a better experience for all users.
By carefully selecting your strategy, leveraging robust tools like Redis for distributed environments, and adhering to best practices, you can build an API Gateway that stands strong against surges in demand and potential abuse. This proactive engineering mindset is central to how we approach API integration and full-stack web app development at Muhyo Tech, ensuring long-term stability and reducing operational stress.