


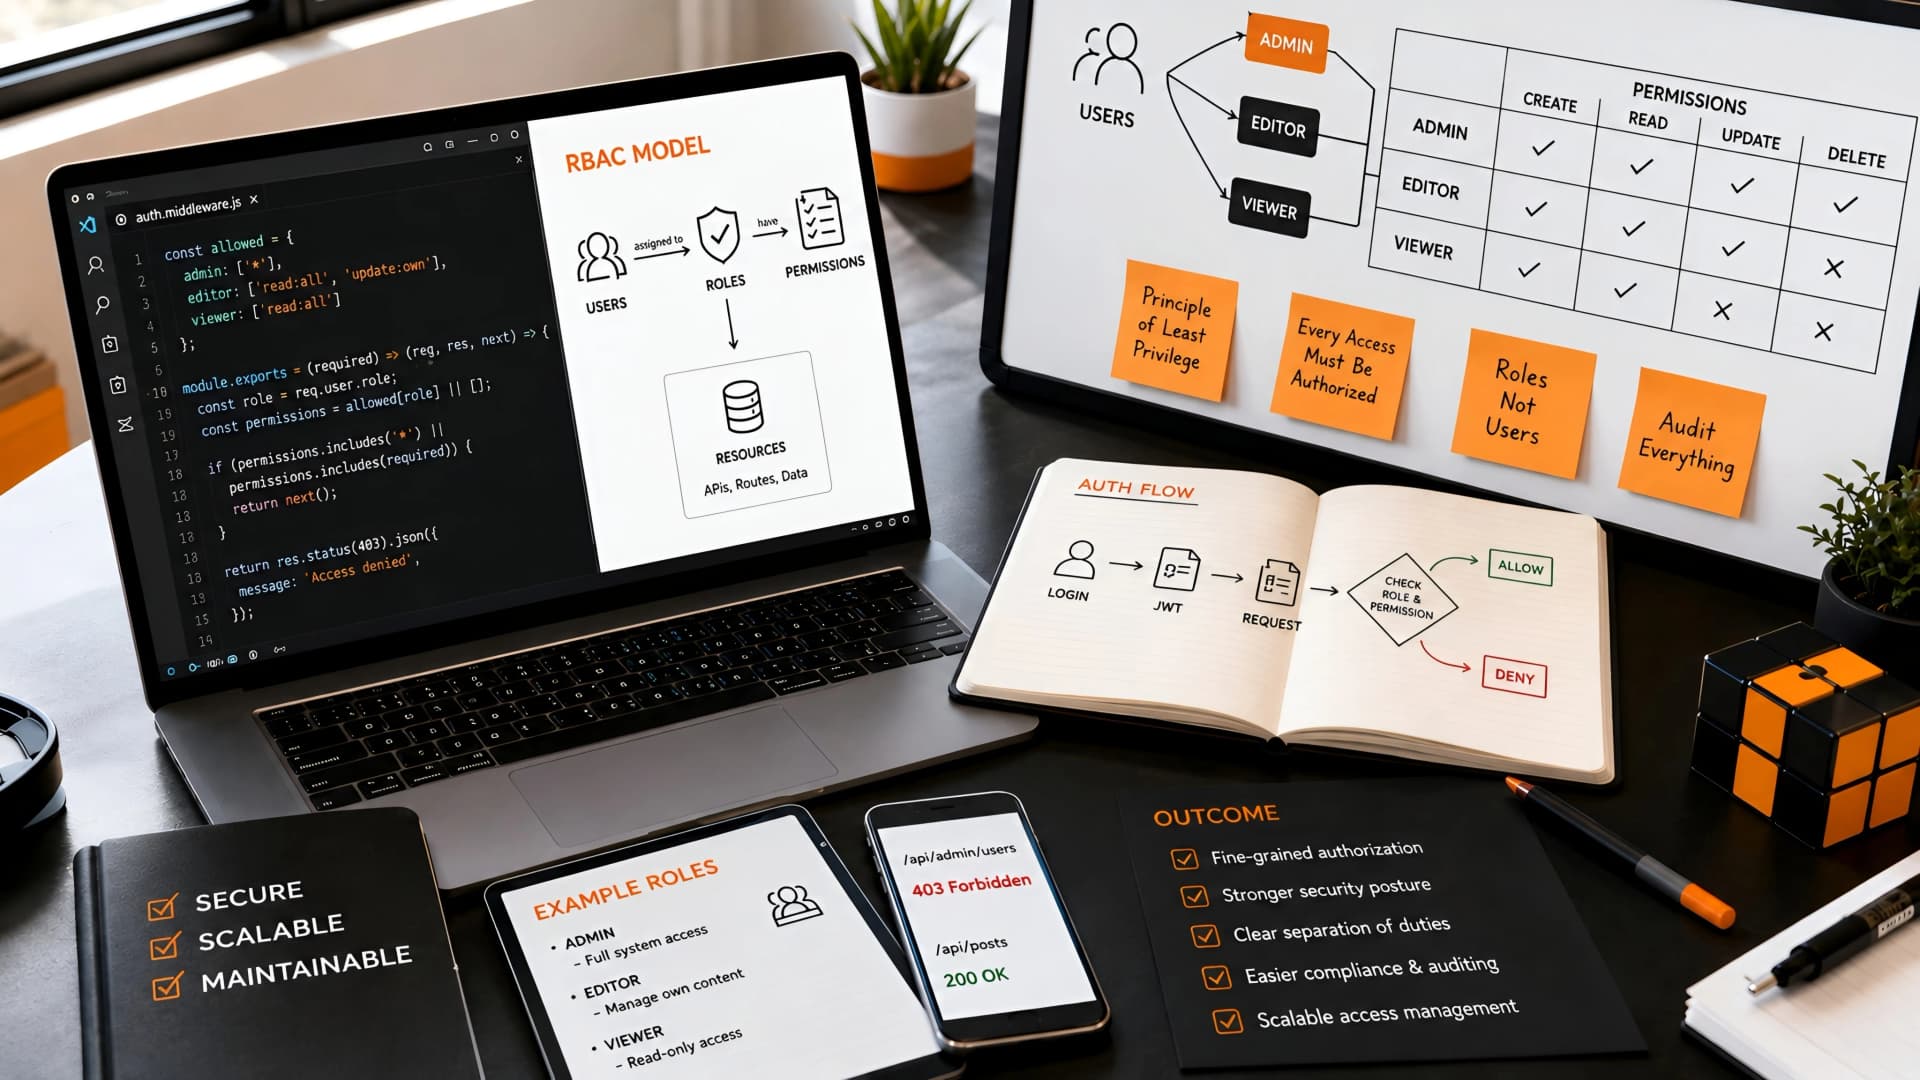
One of the most common headaches in web application development is managing user permissions. Without a clear strategy, authorization logic quickly devolves into a spaghetti of conditional statements, becoming a nightmare to maintain and a breeding ground for security vulnerabilities.
This is where Role-Based Access Control (RBAC) offers a structured, scalable solution. It allows us to define what users can do based on the roles they hold, rather than managing permissions for each individual user.
Understanding the RBAC Core Principle
At its heart, RBAC simplifies authorization by abstracting permissions. Instead of directly assigning permissions to users, we assign permissions to roles.
Users are then assigned one or more roles. This creates a clear hierarchy: users have roles, and roles have permissions. This fundamental separation makes managing access much more predictable and robust.
Designing Your MERN RBAC Architecture
Implementing RBAC in a MERN stack application requires thoughtful schema design and middleware integration. We typically start by defining our roles and the granular permissions associated with each.
For a detailed look at the broader authentication landscape, including how RBAC fits in, you might find our MERN Stack Authentication & Authorization: An Engineering Deep Dive article insightful.
Defining Roles and Permissions in MongoDB
In MongoDB, we can represent roles and permissions in several ways. A common approach involves embedding roles directly into the User schema or creating a separate Role schema to manage permissions dynamically.
For simplicity and flexibility, especially in larger applications, a dedicated Role model often proves superior. This model would define the role name (e.g., 'admin', 'editor', 'viewer') and an array of associated permissions (e.g., 'user:read', 'product:write', 'settings:update').
Here’s a simplified example of how we might structure our MongoDB schemas:
User Model (User.js):
const userSchema = new mongoose.Schema({
  username: { type: String, required: true, unique: true },
  email: { type: String, required: true, unique: true },
  password: { type: String, required: true },
  roles: [{ type: mongoose.Schema.Types.ObjectId, ref: 'Role' }]
});
Role Model (Role.js):
const roleSchema = new mongoose.Schema({
  name: { type: String, required: true, unique: true }, // e.g., 'admin', 'editor', 'viewer'
  permissions: [{ type: String, required: true }] // e.g., ['user:read', 'user:write', 'product:read']
});
This setup allows a user to have multiple roles, and each role can have multiple permissions. This many-to-many relationship provides significant flexibility for defining complex access policies.
Implementing Authorization Middleware with Express.js
The real power of RBAC comes alive in our Express.js backend. We implement authorization logic using middleware functions that check a user's roles and permissions before allowing access to specific routes or resources.
After a user is authenticated (e.g., via JWT), their roles and permissions can be attached to the req.user object. This makes them readily available for subsequent authorization checks.
Creating a checkPermission Middleware
Our authorization middleware needs to perform two key tasks: retrieve the user's roles and then verify if those roles collectively possess the required permission for the requested action.
We typically design a flexible middleware that accepts an array of required permissions. This allows us to protect routes with very specific access rules.
// authMiddleware.js

const User = require('../models/User');
const Role = require('../models/Role');

const checkPermission = (requiredPermissions) => async (req, res, next) => {
  try {
    if (!req.user || !req.user._id) {
      return res.status(401).json({ message: 'Authentication required.' });
    }

    const user = await User.findById(req.user._id).populate('roles');
    if (!user) {
      return res.status(404).json({ message: 'User not found.' });
    }

    const userPermissions = new Set();
    user.roles.forEach(role => {
      role.permissions.forEach(permission => userPermissions.add(permission));
    });

    const hasAllRequiredPermissions = requiredPermissions.every(perm =>
      userPermissions.has(perm)
    );

    if (hasAllRequiredPermissions) {
      next();
    } else {
      res.status(403).json({ message: 'Forbidden: Insufficient permissions.' });
    }
  } catch (error) {
    console.error('Authorization error:', error);
    res.status(500).json({ message: 'Server error during authorization.' });
  }
};

module.exports = checkPermission;
This middleware fetches the user, populates their roles, and then collects all unique permissions. It then checks if *all* the requiredPermissions are present in the user's collective set of permissions.
Protecting Routes and Data
With our middleware in place, protecting routes becomes straightforward. We simply apply the checkPermission middleware to any route that requires specific access levels.
For example, to protect an admin-only endpoint that updates product information, we might use it like this:
// productRoutes.js

const express = require('express');
const router = express.Router();
const { authenticateJWT } = require('../middleware/auth'); // Your JWT authentication middleware
const checkPermission = require('../middleware/checkPermission');

router.put('/products/:id', authenticateJWT, checkPermission(['product:write', 'product:update']), async (req, res) => {
  // Logic to update product
  res.status(200).json({ message: 'Product updated successfully.' });
});

router.get('/users', authenticateJWT, checkPermission(['user:read']), async (req, res) => {
  // Logic to fetch all users
  res.status(200).json({ message: 'List of users.' });
});
This approach ensures that only authenticated users with the 'product:write' AND 'product:update' permissions can modify products. Similarly, only users with 'user:read' can fetch user lists.
Trade-offs and Considerations
While RBAC offers significant advantages, it's not without its trade-offs. The initial setup requires careful planning of roles and permissions.
Overly granular permissions can lead to a large number of permissions to manage, increasing complexity. Conversely, too few permissions might limit flexibility. We often find a balance by grouping related actions.
Performance is another consideration; fetching roles and permissions on every request can add overhead. Caching user permissions after authentication can mitigate this, especially in high-traffic applications. At Muhyo Tech, we often optimize these checks, sometimes embedding simplified role information directly into JWTs, trading off some flexibility for speed.
Business Value: Security and Scalability
Implementing RBAC effectively translates directly into tangible business value. It provides granular control over user access, significantly enhancing application security by preventing unauthorized actions.
For founders and business owners, this means less risk of data breaches and compliance issues. For development teams, it simplifies permission management, making the application easier to scale and maintain as new features or user types are introduced.
A well-architected RBAC system reduces the administrative burden of managing user access and allows the team to focus on building features, not battling authorization bugs. This is a core part of our approach to building reliable, long-term web applications.